Mobile Security Alert: Phishing Campaigns Threaten US Users
Recent mobile phishing campaigns are a growing threat, impacting a significant portion of US smartphone users. This article explains how these attacks work, how to recognize them, and the essential steps you can take to protect your personal information and device from compromise.
Por: Michael Sete em 21 de agosto de 2026
Última atualização em: agosto 24, 2026
A critical mobile security alert has been issued, highlighting new and aggressive mobile phishing campaigns that are actively targeting users across the United States. These sophisticated attacks are not just theoretical; they are impacting a significant percentage of smartphone owners, with estimates suggesting as many as 15% of U.S. smartphone users have been exposed or victimized. Understanding the nature of these threats and how to defend against them is more crucial than ever in our increasingly connected world. Cybercriminals are constantly refining their tactics, making it essential for everyone to stay informed and vigilant about the digital dangers lurking in their pockets.
The rise of mobile device usage has unfortunately created a fertile ground for malicious actors. Our smartphones hold a vast amount of personal and sensitive information, from banking details to private communications, making them prime targets. These latest mobile phishing campaigns exploit our trust and reliance on these devices, often using convincing lures to trick individuals into compromising their data. Recognizing the signs of a phishing attempt and implementing robust security practices can make all the difference in protecting your digital life from these pervasive and evolving threats.
Understanding the Evolving Threat of Mobile Phishing Campaigns
Mobile phishing campaigns represent a significant and growing danger in the cybersecurity landscape. Unlike traditional email phishing, these attacks are specifically designed to exploit the unique characteristics of mobile devices and user behavior. They often come in the form of SMS messages (smishing), messaging app links, or even fake app notifications, making them harder to distinguish from legitimate communications. The casual nature of mobile interaction, combined with smaller screens and less obvious warning signs, contributes to their effectiveness. Users might quickly tap a link without scrutinizing it as closely as they would on a desktop computer, leading to immediate compromise.
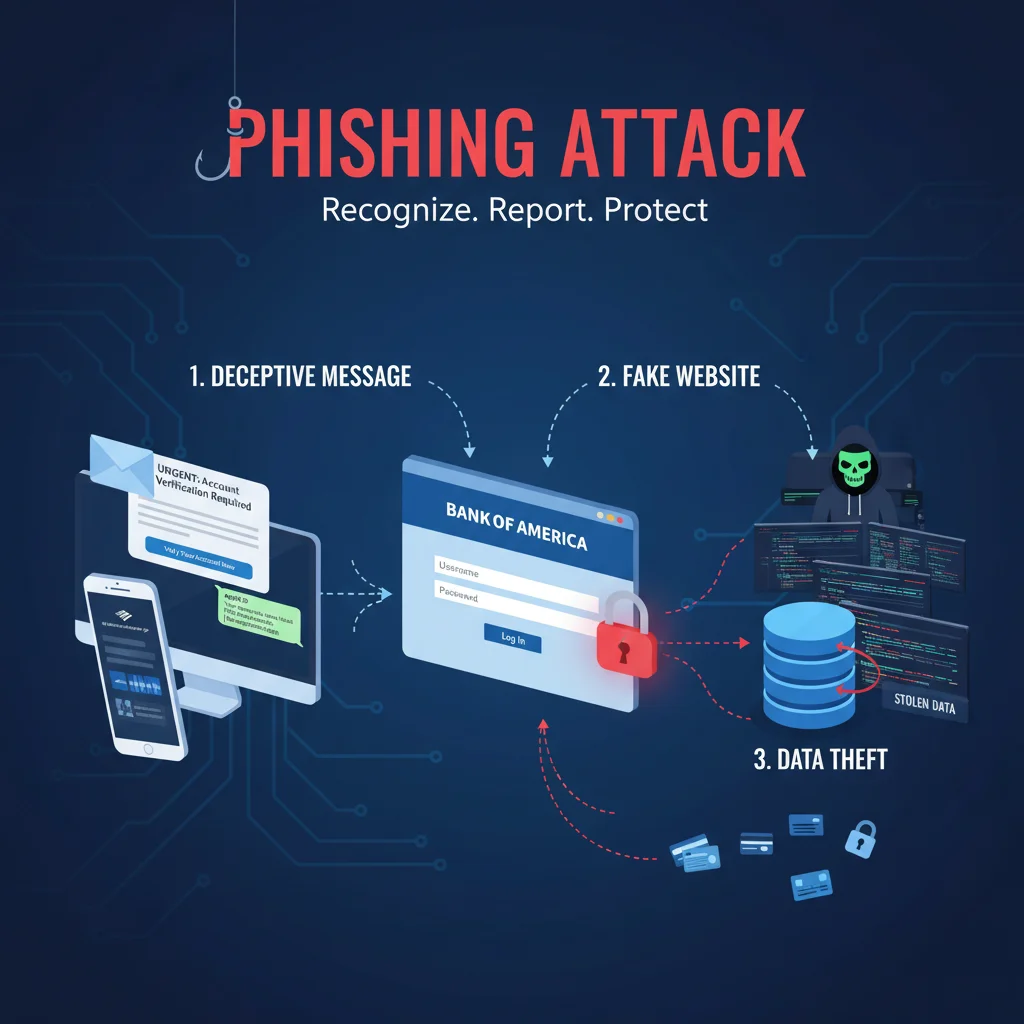
These campaigns are becoming increasingly sophisticated, employing social engineering tactics that play on urgency, fear, or curiosity. For instance, messages might impersonate banks, government agencies, or well-known delivery services, claiming issues with an account, a package delivery, or an urgent security update. The goal is always the same: to trick you into revealing personal information, such as login credentials, credit card numbers, or other sensitive data. Once this information is obtained, attackers can use it for identity theft, financial fraud, or to gain unauthorized access to your various online accounts, causing significant damage and distress.
The sheer volume and targeted nature of these recent mobile phishing campaigns are what make them particularly concerning. Attackers are using automated tools to send out millions of messages, hoping to ensnare a percentage of recipients. Even a small success rate can yield a large harvest of compromised data. Moreover, these campaigns often evolve rapidly, changing their lures and techniques to bypass detection methods, meaning that what was a recognizable phishing attempt yesterday might look entirely different today. Staying current with the latest tactics used by cybercriminals is an ongoing challenge but a necessary one for effective mobile security.
Common Tactics Used in Recent Mobile Phishing Attacks
The recent surge in mobile phishing campaigns showcases a range of deceptive tactics designed to trick even the most cautious users. One of the most prevalent methods involves sending SMS messages that appear to come from legitimate organizations. These messages often include a sense of urgency, urging the recipient to click a link to resolve an issue, confirm a delivery, or update personal information. The links typically lead to convincing but fake websites that mimic official portals, designed solely to capture your credentials. Because these messages blend in with regular text conversations, they can be particularly difficult to spot for an unsuspecting user.
Another common tactic leverages popular apps and services. Attackers might send messages impersonating social media platforms, streaming services, or online retailers, claiming account irregularities or special offers. These messages often prompt users to log in through a provided link, which, again, directs them to a fraudulent site. The convenience of single sign-on features on mobile devices can also be exploited, as users might be less inclined to re-verify a URL when presented with a familiar login screen. This reliance on brand recognition is a powerful tool in the phisher’s arsenal, making it critical to question every unsolicited communication.
Deceptive Link Shorteners and QR Codes
Link Shorteners: Cybercriminals frequently use URL shorteners to disguise malicious links. While link shorteners have legitimate uses, they also hide the true destination of a web address, making it impossible to tell if a link is safe without clicking it first. Always be wary of shortened links from unknown sources.
QR Codes: Phishing can also manifest through malicious QR codes. These codes might appear on physical flyers, advertisements, or even in emails, promising discounts or information. Scanning a compromised QR code can lead to malware downloads or phishing sites, bypassing some of the traditional warning signs of a text-based link.
Impersonation: Attackers often go to great lengths to impersonate known entities, from using similar-looking logos to crafting messages that mimic the language and tone of official communications. This level of detail makes their schemes more believable and harder to detect without close inspection.
These evolving tactics highlight the need for constant vigilance and a healthy skepticism towards unsolicited messages and links on your mobile device. Always take a moment to pause and verify before clicking or entering any personal information.
Identifying Red Flags: How to Spot a Phishing Attempt
Detecting a mobile phishing attempt requires a keen eye and an understanding of common red flags. One of the most immediate indicators is an unexpected message that demands urgent action. Phishers often create a sense of panic or excitement to bypass your critical thinking. For instance, a text claiming your bank account has been frozen and requiring immediate verification via a link should raise an alarm. Legitimate organizations rarely request sensitive information or account details through unsolicited text messages or emails.
Another crucial red flag is a suspicious link. Before clicking any link, hover over it (if possible on your device) or long-press it to preview the URL. Look for discrepancies between the displayed text and the actual destination. Malicious links often contain misspellings, extra characters, or domains that are slightly different from the official ones (e.g., ‘amaz0n.com’ instead of ‘amazon.com’). If the URL doesn’t look exactly right, it’s safer to avoid it. Even if a link appears legitimate, it’s always best to navigate directly to the official website or app rather than clicking through an unsolicited message.
Poor grammar, spelling errors, and awkward phrasing in messages are also strong indicators of a phishing attempt. While some sophisticated campaigns might have flawless language, many still contain telltale mistakes that legitimate businesses would never make. Additionally, be wary of messages that ask for personal information such as passwords, Social Security numbers, or credit card details directly. Reputable companies will not ask for this sensitive data via text or email. If you receive such a request, it’s almost certainly a scam. Trust your instincts; if something feels off, it probably is.
Proactive Measures to Protect Your Smartphone Data
Protecting your smartphone from the relentless threat of mobile phishing campaigns requires a multi-layered approach involving both technological safeguards and smart user habits. One of the most effective proactive measures is to keep your device’s operating system and all installed applications updated. Software updates often include critical security patches that fix vulnerabilities exploited by cybercriminals. Enabling automatic updates ensures you always have the latest protections without having to manually check.
Another vital step is to use strong, unique passwords for all your online accounts and enable two-factor authentication (2FA) wherever possible. Even if phishers manage to steal your login credentials, 2FA provides an additional layer of security, making it significantly harder for them to access your accounts. Consider using a password manager to help create and store complex passwords securely. This reduces the risk of credential stuffing attacks, where compromised credentials from one site are used to try and log into others.
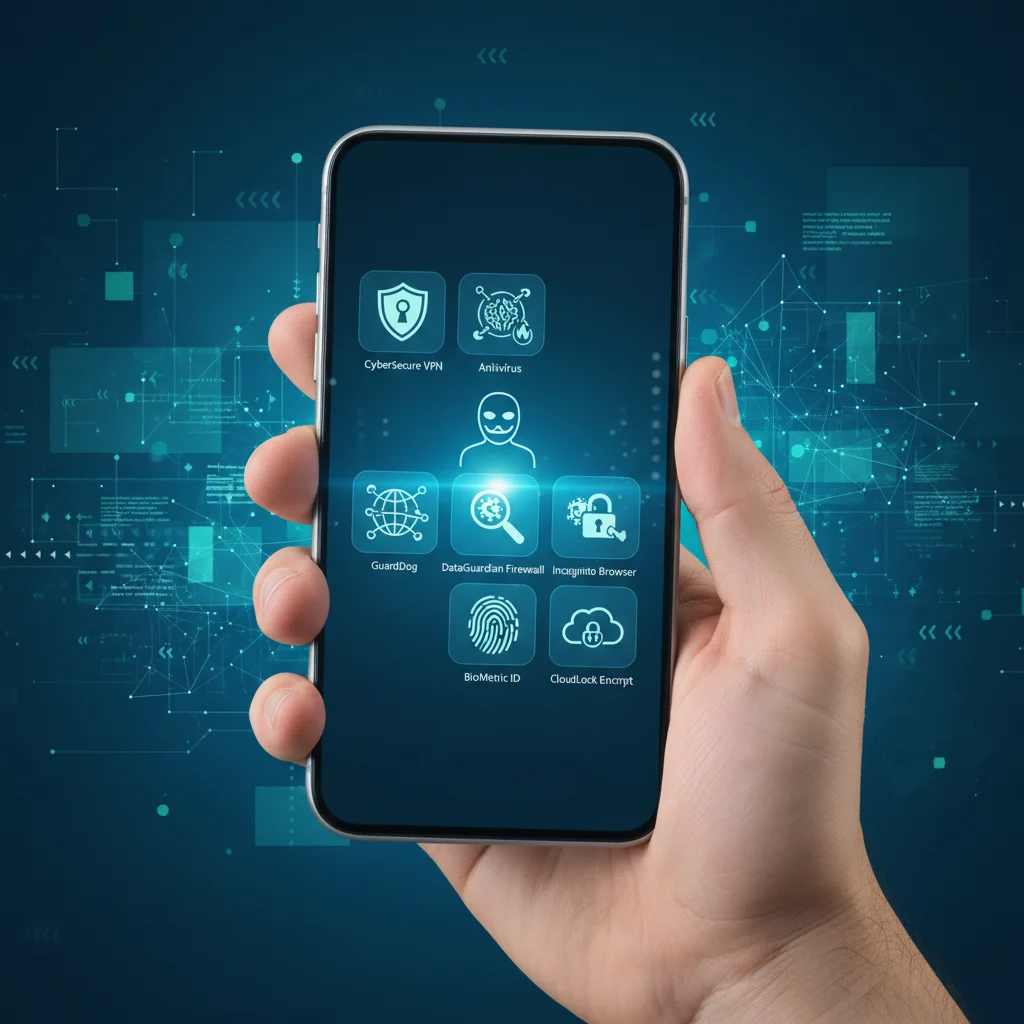
Installing reputable mobile security software can also provide an essential defense. These applications can detect and block malicious websites, scan for malware, and alert you to suspicious activity. While not foolproof, they add an extra layer of protection against emerging threats. Furthermore, exercise caution when connecting to public Wi-Fi networks. These networks are often unsecure and can be easily intercepted by attackers. If you must use public Wi-Fi, consider using a Virtual Private Network (VPN) to encrypt your internet traffic and protect your data from eavesdropping.
What to Do If You Suspect You’ve Been Phished
Despite best efforts, anyone can fall victim to a sophisticated mobile phishing campaign. If you suspect you’ve clicked a malicious link or entered your information on a fake website, immediate action is crucial to minimize potential damage. The very first step is to disconnect your device from the internet, either by turning off Wi-Fi and mobile data or by switching to airplane mode. This can prevent further data transmission or the installation of malware. The quicker you act, the better your chances of limiting the impact of the attack.
Next, change all potentially compromised passwords immediately. Focus on critical accounts first, such as banking, email, social media, and any other services where you might have reused passwords. If you entered credit card information, contact your bank or credit card company to report potential fraud and monitor your statements closely for any unauthorized transactions. If you used two-factor authentication, ensure that your 2FA methods are still secure and consider regenerating recovery codes or changing your 2FA settings if you believe they might have been compromised as well.
It’s also important to scan your device for malware using a reputable mobile security application. If any malicious software is detected, follow the app’s instructions to remove it. You might also consider performing a factory reset as a last resort if you cannot remove the malware, but be sure to back up your important data first. Finally, report the phishing attempt. Forward suspicious text messages to 7726 (SPAM) in the U.S. and report phishing websites to official government agencies like the Anti-Phishing Working Group (APWG) or the FTC. Reporting helps authorities track these campaigns and protect others from falling victim.
Frequently Asked Questions
What exactly is mobile phishing?
Mobile phishing is a type of cyberattack where criminals use deceptive messages, typically via SMS or messaging apps, to trick smartphone users into revealing personal information or installing malware. These messages often impersonate trusted entities to appear legitimate.
How can I tell if a text message is a phishing attempt?
Look for red flags like unexpected messages, urgent requests for personal data, suspicious links (hover or long-press to preview), poor grammar, and generic greetings. Legitimate organizations rarely ask for sensitive information via unsolicited texts.
What should I do if I accidentally click a phishing link?
Immediately disconnect your device from the internet, change any passwords you might have entered, contact your bank if financial details were shared, and scan your device for malware. Report the incident to relevant authorities.
Are mobile security apps really effective against phishing?
Yes, reputable mobile security apps can be very effective. They often include features like malicious website blocking, malware scanning, and real-time threat detection, adding a crucial layer of defense against various cyber threats, including phishing.
Why are mobile phishing campaigns so common now?
Mobile phishing is on the rise because smartphones are ubiquitous, contain vast amounts of personal data, and users often interact with them more casually, making them susceptible to social engineering tactics. Attackers exploit this convenience and trust.
The increasing prevalence of mobile phishing campaigns serves as a stark reminder that our digital security demands constant attention, especially concerning our smartphones. With an estimated 15% of U.S. smartphone users facing these sophisticated threats, the need for heightened awareness and proactive defense has never been more critical. These campaigns are cunning, often mimicking trusted sources and exploiting human psychology to steal valuable personal data. By understanding the tactics employed by cybercriminals, recognizing the tell-tale signs of a phishing attempt, and implementing robust security practices, individuals can significantly reduce their risk of becoming a victim. This includes keeping software updated, using strong unique passwords with 2FA, and installing reliable mobile security applications.
Should you ever suspect that you’ve been targeted or compromised, acting swiftly is paramount. Disconnecting from the internet, changing passwords, and reporting the incident are crucial steps to mitigate damage and help authorities combat these evolving threats. Staying informed, exercising skepticism towards unsolicited messages, and leveraging available security tools are your best defenses in this ongoing digital battle. Let’s collectively commit to a more secure mobile experience by empowering ourselves with knowledge and taking decisive action against mobile phishing campaigns.